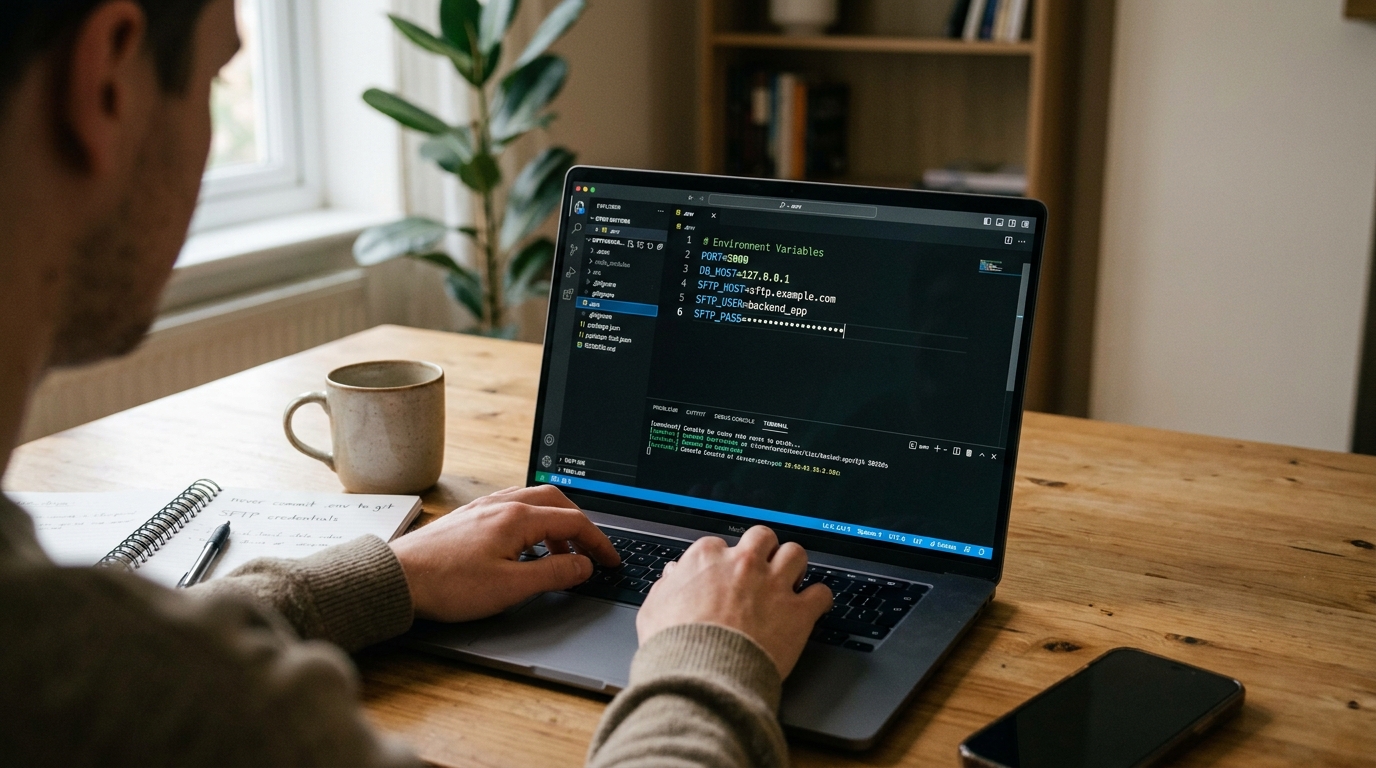
How to Configure Environment Variables and SFTP Credentials Securely in Modern Backends: A Beginner's Technical Guide
Hardcoding sensitive credentials like SFTP passwords, API secrets, and database strings directly into source code remains one of the primary causes of severe security breaches. When hardcoded secrets are accidentally committed to version control repositories, they expose production infrastructure to automated credential-scraping bots within minutes.
Modern backend engineering requires a strict separation between application code and operational configuration. By using environment variables alongside dedicated secret management techniques, you can safely handle SFTP credentials and system variables across development, staging, and production environments.
The Golden Rule of Configuration Security
The fundamental principle of secure backend design is to treat application code as immutable and environment-agnostic. Your codebase should be capable of being made open source at any moment without leaking a single credential.
Environment variables are dynamic key-value pairs set at the operating system or container level. Instead of embedding passwords directly inside application scripts, the application reads these values from its execution environment at runtime.
Step 1: Manage Local Environment Variables with .env Files
During local development, developers use .env files to emulate production environment variables without modifying system-level settings.
Create a .env file in your project's root directory:
Ini, TOML
Step 2: Prevent Environment Leakage via .gitignore
The single most critical step when using .env files is ensuring they are never tracked by Git.
Add the .env file to your root .gitignore file immediately:
Code snippet
To help team members understand which configuration variables are required, commit a safe boilerplate template named .env.example containing empty values:
Ini, TOML
Step 3: Use SSH Key-Based Authentication for SFTP
Password-based SFTP authentication is vulnerable to brute-force attacks and requires storing raw passwords in your configuration files. Modern backends should always authenticate via SSH key pairs.
- Generate a dedicated, non-interactive SSH key pair on your machine using the Ed25519 algorithm:
Bash
- Public Key Deployment: Copy the contents of
sftp_backend_key.pubonto your remote SFTP server inside the target user's~/.ssh/authorized_keysfile. - Private Key Storage: Store the private key (
sftp_backend_key) securely. In containerized environments or CI/CD pipelines, pass the raw content of the private key as a base64-encoded environment variable (SFTP_PRIVATE_KEY_BASE64) to avoid mounting physical files.
Step 4: Access Environment Variables in Node.js and PHP
Once variables are set in the environment or .env file, read them securely inside your backend logic using native runtimes or configuration libraries.
Node.js Backend Example
In Node.js, load variables using the dotenv package and parse them safely:
JavaScript
PHP Backend Example
In PHP, use vlucas/phpdotenv to load local configurations safely into $_ENV:
PHP
Step 5: Production Deployment and Cloud Secret Managers
In production, never upload .env files to cloud servers. Instead, inject environment variables directly into the application process using cloud infrastructure tools:
- Docker & Container Orchestration: Inject variables using
environmentfields in Docker Compose or KubernetesSecretmanifests mounted directly to application pods. - Cloud Platform Managers: Use specialized key-management solutions such as AWS Secrets Manager, HashiCorp Vault, or Google Secret Manager. These services store secrets encrypted at rest and inject them dynamically into runtime processes at startup.
- CI/CD Pipelines: Define SFTP deployment keys inside secure repository settings (e.g., GitHub Actions Secrets or GitLab CI/CD Variables) so build scripts can deploy files without exposing authentication credentials to developers.
Security Audit Checklist
Before deploying any backend service handling remote file synchronization:
- Search your entire git commit history for accidentally committed API keys, raw SSH private keys, or
.envfiles. - Confirm that
.envis listed inside.gitignore. - Disable password authentication on the remote SFTP server, forcing key-only SSH connections.
- Restrict the file permissions of SSH private keys locally using
chmod 600 ~/.ssh/sftp_backend_key. - Rotate production SFTP keys periodically and immediately revoke keys when team members leave your organization.